
Software Testing Types: Complete Guide & Automation in 2026
Discover how Agentic AI and LLM testing are transforming QA in 2026. A complete guide on levels, types, strategies, and automated testing.
Why is the software testing phase so critical?
The software testing phase is essential because it guarantees the quality, functionality, and security of a system before its public release. In 2026, where systems leverage Agentic Artificial Intelligence, the cost of software failure is not merely financial—it severely damages brand reputation and operational integrity. High investment in quality assurance is justified by the need to test not only happy paths, but also the emergent behaviors of increasingly autonomous software systems.
Difference Between Error, Defect, and Failure
| Term | Definition | Real-World Example |
|---|---|---|
| Error | A human mistake or oversight during software design or coding. | A developer writing an incorrect comparison operator in source code. |
| Defect (Bug) | The flaw resulting from an error, causing unexpected behavior in the software. | A submit button failing to trigger form validation due to bad logic. |
| Failure | Occurs when the live application exhibits incorrect behavior to the end user. | A production server crashing while processing real-time transaction spikes. |
Levels of Software Testing
Software testing is executed across distinct architectural levels throughout the development cycle:
- Unit Testing: Executed by developers during coding to verify isolated modules and functions.
- System Testing: Conducted by QA engineering teams to validate end-to-end system compliance with specified requirements.
- Integration Testing: Tests communication between integrated components and external services (e.g., third-party APIs).
- Acceptance Testing: Performed with product owners or key stakeholders to confirm the software satisfies business needs.
Software Testing Strategies
Testing strategies are classified into distinct methodologies based on timing, goals, and execution scope.
Dynamic Testing
Executes code directly to uncover runtime failures. It covers broad execution paths but requires dedicated execution environments.
Static Testing
Evaluates code and artifacts without execution, including code reviews and static analysis. Cost-effective early in the lifecycle.
Preventive Testing
Initiated prior to code implementation to prevent defects before they occur, drastically reducing post-deployment costs.
Reactive Testing
Executed in response to identified bugs. Useful for edge cases but potentially expensive if critical bugs reach production.
White Box
Inspects internal code structures. In 2026, AI-enhanced static analysis tools identify security flaws prior to code commit.
Black Box
Tests functionality from the user's perspective. Autonomous QA agents execute black box scenarios with unprecedented speed.
Gray Box
Combines internal structural knowledge with external user perspective to validate complex API data pipelines.
Agentic QA: The AI Revolution in 2026
The era of reactive QA is over.
Replace brittle static scripts with Agentic QA. Autonomous AI agents interact with your web and mobile applications like real human users, backed by machine precision.
- Autonomous Flow Discovery: AI continuously explores unmapped user paths and unexpected edge cases.
- Self-Healing Test Suites: When UI element IDs or layouts update, AI auto-heals tests, eliminating flaky test failures.
- Intelligent Load & Stress Simulations: Simulates millions of non-linear user behaviors under unpredictable network conditions.
Validating Intelligence: LLM Testing and Hallucination Control
The 2026 Warning: The Era of AI-Generated Code & Prompts
Today, the barrier between traditional development and prompt-driven engineering has largely vanished. Entire codebases, features, and UI modifications are pushed daily through AI prompts.
This environment makes automated testing more critical than ever.
With AI hallucinations on the rise, a single prompt modification risks breaking unexpected dependencies and compromising system integrity. In 2026, automated testing is not just about adding features—it protects digital assets against the probabilistic errors of Large Language Models.
Unlike deterministic code, AI outputs are inherently probabilistic. At Shinier, we implement rigorous testing methodologies to eliminate risks:
Hallucination & RAG Testing
Ensures LLM models stay grounded strictly within proprietary knowledge bases without inventing facts.
Prompt Injection Defense
Tests system resilience against malicious prompt injection attacks attempting to hijack model behavior.
Shinier 2026 Integrity Protocol:
- Bias Auditing: Evaluation and mitigation of algorithmic bias in generated content.
- Model Regression Safeguards: Ensuring new LLM versions do not degrade overall application quality.
- Context Validation: Precision & Recall verification across retrieval-augmented generation pipelines.
Software Testing Methods
Testing methods define structured approaches to system evaluation. Each method addresses specific operational parameters to guarantee complete coverage.
- Step-by-Step Testing: Evaluates system workflows sequentially against expected outputs.
- Pairwise Testing: Tests combinatorics of input parameters to catch multi-variable interaction bugs.
- Cause-Effect Graphing: Maps relationships between potential system inputs (causes) and outputs (effects).
- Equivalence Partitioning: Groups input data into functional classes to optimize test suite size.
- Boundary Value Analysis: Validates application stability at parameter limits and edge values.
12 Key Types of Software Testing
Shinier organizes software testing into 12 core types covering every aspect of modern application health:
Volume
Tests system stability when processing massive volumes of data.
Stress
Evaluates application limits and behavior under extreme load conditions.
Load
Measures system performance under expected and peak concurrent traffic.
Exploratory
Unscripted testing designed to uncover unanticipated edge-case defects.
Acceptance
Validates that software meets business specifications and user expectations.
Performance
Assesses response times, throughput, and system resource efficiency.
Confirmation
Verifies that previously reported bugs are permanently resolved.
Recovery
Tests system resilience and failover recovery speed after crashes.
Security
Audits system vulnerabilities against unauthorized access and cyber threats.
Smoke
Rapid build-verification tests confirming overall build stability.
Functional
Verifies that core feature specifications function as intended.
Regression
Ensures new code changes do not break existing stable functionality.
Shinier's Exclusive Testing Methodology
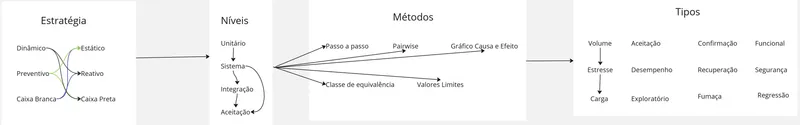
Shinier developed a proprietary diagramming framework to map and optimize end-to-end testing processes. Refined across years of engineering practice and corporate training programs, this methodology combines continuous automated pipelines with agentic QA to guarantee maximum test coverage, accelerating deployment velocity while maintaining uncompromised quality.
Referências
- PRESSMAN, Roger S. Software Engineering: A Practitioner's Approach. 8th ed. McGraw-Hill, 2014. Covers the software development life cycle, cost management, and quality assurance best practices including software testing. McGraw-Hill
- SOMMERVILLE, Ian. Software Engineering. 10th ed. Pearson, 2015. Comprehensive reference covering requirements engineering through to software validation and verification. Pearson
- BROOKS, Frederick P. The Mythical Man-Month: Essays on Software Engineering. Anniversary ed. Addison-Wesley, 1995. Classic work exploring project complexity, estimation myths, and testing realities. UMich
- BOEHM, Barry W. Software Engineering Economics. Prentice Hall, 1981. Landmark foundational study linking quality, testing effort, and software development cost metrics. Amazon
Modernize your QA process with AI
Shinier specializes in transforming legacy testing workflows into modern, autonomous agentic QA infrastructures. Reduce costs and deploy with full confidence in 2026.
Get QA Consulting